AI Security
Last Updated:
Deepak Singla

IN this article
Support agents are using unauthorized AI tools like ChatGPT and Gemini with sensitive customer data, costing companies an average of $2.8M a year in breaches and fines. Fini's 7-step governance framework, built from 200+ enterprise rollouts, gives CX, compliance, and security leaders a way to control that risk without slowing agents down.
Executive Summary
Shadow AI, the unauthorized use of tools like ChatGPT and Gemini by support agents, is a quiet but costly threat. It’s fast, convenient, and completely off the radar of IT and compliance teams.
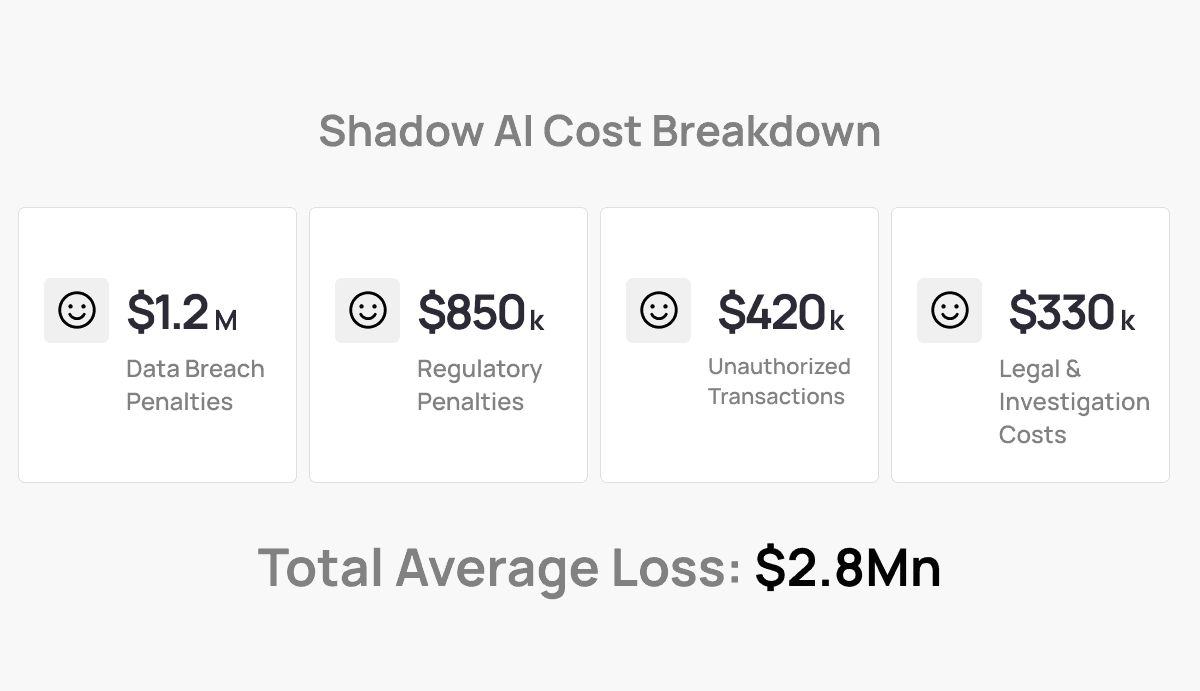
The result? An average $2.8M annual loss per company.
That figure keeps climbing. IBM's 2026 data breach report puts the average cost of a shadow AI linked breach at $5.39M, up from $4.99M overall, with shadow AI linked incidents rising from 20% to 43% of all AI-related breaches year over year.
In this expert guide, we’ll show you how to stop Shadow AI before it spirals, using Fini’s proven 7-step governance framework adopted by 200+ companies.
Quick stats:
These figures come from Fini's own analysis of 200+ enterprise governance rollouts, cross-checked against the IBM 2026 data breach findings cited below.
Shadow AI: The $2.8M Support Problem
Shadow AI occurs when employees adopt generative AI tools without approval from InfoSec or Legal. If you're unfamiliar with what Shadow AI means in a support context, it often starts innocently ("just helping a customer faster"), but leads to serious compliance risks.
Common examples:
Copy-pasting private customer data into personal ChatGPT
Using Claude to write refund or KYC messages
Letting AI generate policy replies without checks
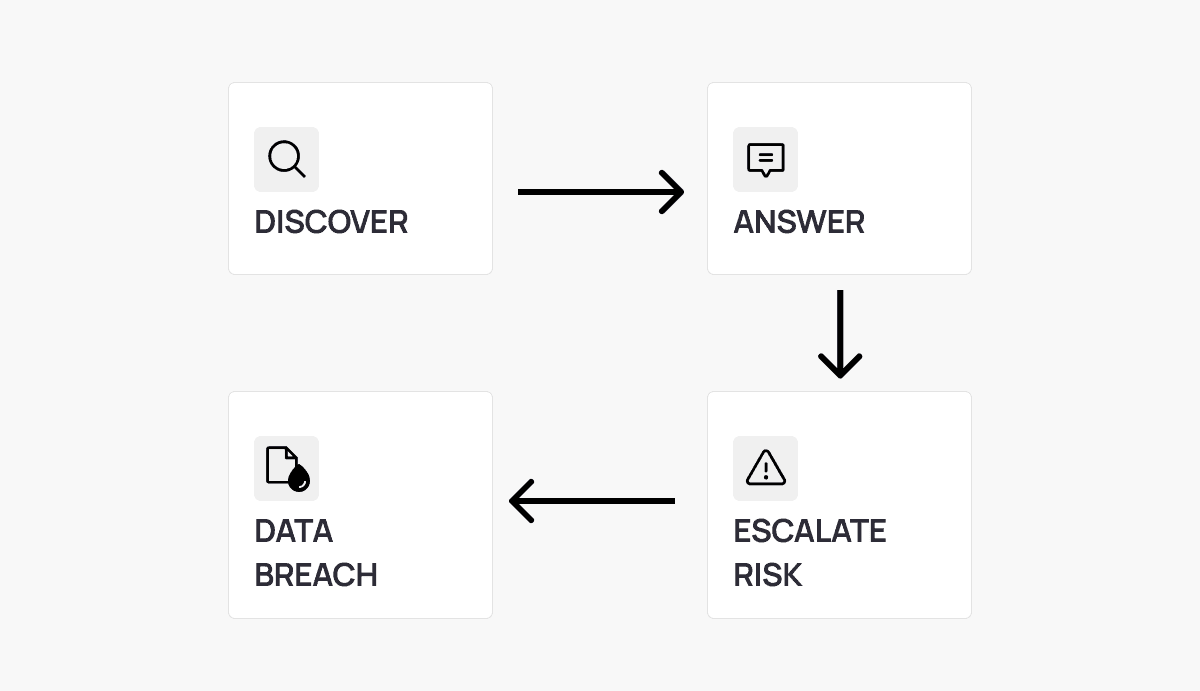
These hacks feel efficient. But they’re invisible, untracked, and non-compliant with AI compliance requirements.
Why Support Teams Are Especially Vulnerable:
Fast-paced environments put speed ahead of security.
For a deeper look into the shift toward autonomous AI support agents, check out our guide on turning e-commerce support into a revenue engine.
Breaking down the $2.8M cost of Shadow AI
Category | Average Annual Cost | Incident Probability |
|---|---|---|
Data Breach Fines | $1.2M | 23% |
Regulatory Penalties | $850K | 18% |
Unauthorized Transactions | $420K | 31% |
Legal & Investigation Costs | $330K | 15% |
Total Annual Risk | $2.8M | 37% |
And that’s just the direct cost.
Indirect costs often overlooked:
Brand damage leading to 15% to 30% churn
Want to know how top companies mitigate refund abuse with AI? Read more about training AI agents for transaction disputes.
The 5 Hidden Risks of Shadow AI
Data Leaks: PII and PCI shared with external AI tools
Compliance Violations: GDPR, HIPAA, EU AI Act breaches
Fraud: Unauthorized refunds or KYC approvals
Lost Trust: Damaged customer relationships
Ops Disruption: Incident response halts day-to-day work
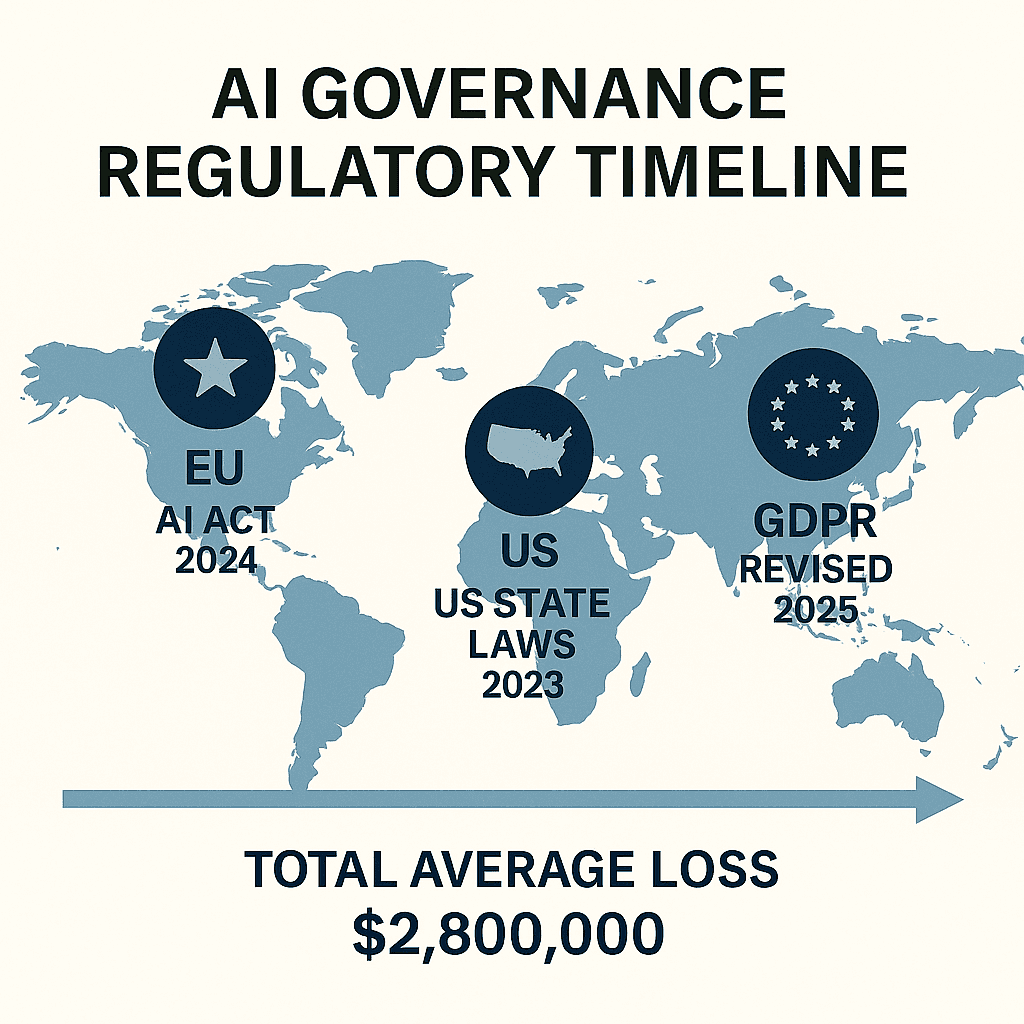
The Regulatory Reality (2026 Update)
Regional Regulatory Key Points
EU AI Act (2024)
Mandatory logs for high-risk AI systems
Fines: up to €35M or 7% of global revenue
GDPR + AI Updates
Right to explanation for AI-led decisions
Enhanced data transparency and consent protocols
U.S. Patchwork Laws
CCPA 2.0: Requires disclosures on automated decision-making
SHIELD Act (NY), BIPA (IL): Enhanced penalties for misuse of customer data in AI models
Where Things Stand in Late 2026
The EU AI Act's high-risk system obligations took effect in August 2026, and regulators are now auditing AI usage logs directly instead of merely reviewing policy documents on paper. Support teams that treated Shadow AI as a future problem are the ones facing active audits today. Teams that already have AI guardrails in place are better positioned to pass these audits without a last-minute scramble.
Regulators increasingly request AI usage logs during routine audits, and not merely after an incident.
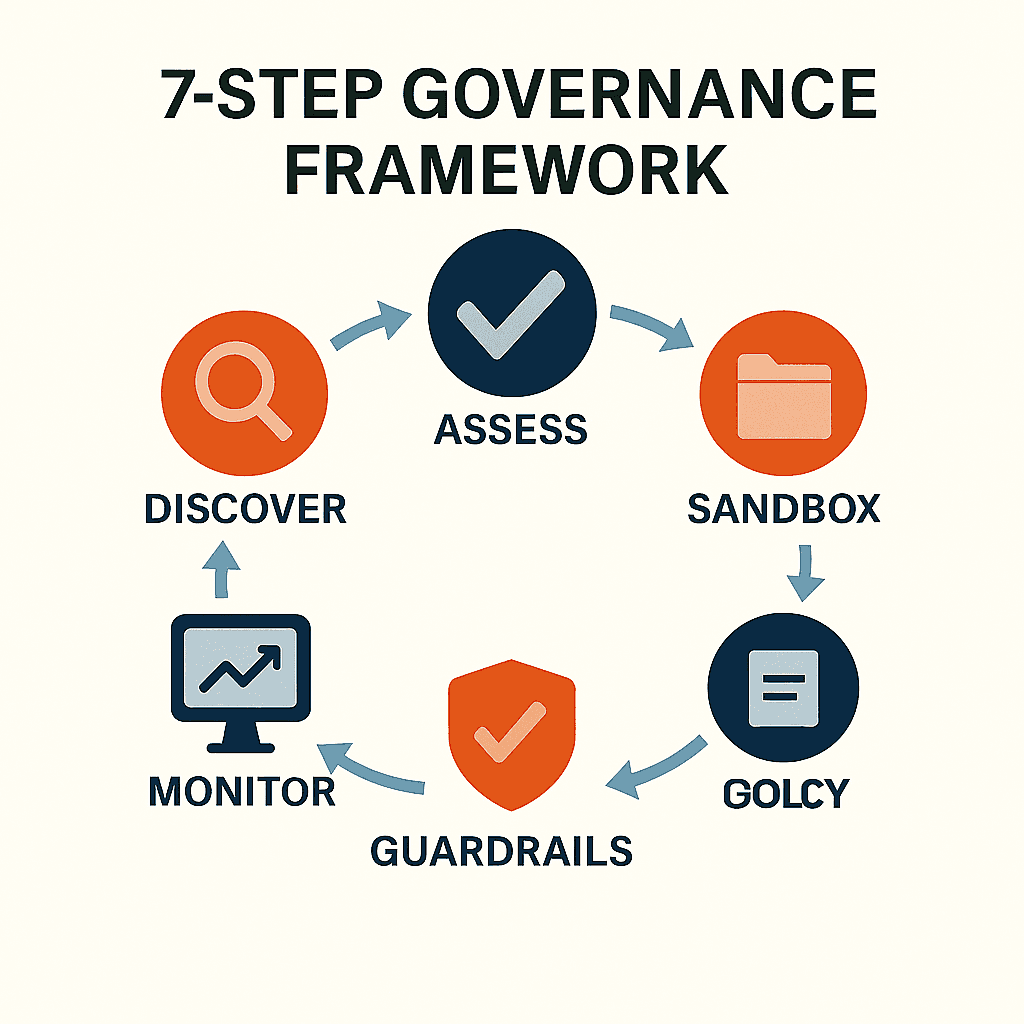
Fini’s Proven 7-Step Shadow AI Governance Framework
This framework has helped over 200 organizations move from risky, ad hoc AI usage to controlled, compliant operations. Speed and agent autonomy stay intact. It builds on the same principles covered in our guide to guardrails in AI support.
Discovery: Map the Unseen Usage
Run browser telemetry and session audits to detect AI tool usage (e.g., ChatGPT, Gemini).
Survey agents and team leads to understand where AI is already part of workflows.
Flag departments or individuals using AI without policy guidance.
Goal: Get a full inventory of where Shadow AI is being used and what data it’s touching.
Risk Assessment: Rank What Matters
Score usage based on data type (PII, PCI, health data), volume, and tool risk profile.
Factor in regulatory exposure (GDPR, HIPAA, CCPA).
Segment into: Low-risk, Conditional, and High-risk usage.
Goal: Know what’s most likely to get you fined or cause a breach, and fix that first.
Secure Sandboxing: Test Before You Trust
Weigh productivity gains vs. compliance trade-offs.
Goal: Allow experimentation, but in a way that’s safe, observable, and compliant.
Clear Policy Design: Define the Guardrails
Draft a tiered AI usage policy:
Approved Use
Conditional Use (e.g., masked data only)
Prohibited Use
Include real-world do’s and don’ts, e.g., “Don’t paste billing disputes into public AI tools.”
Goal: Equip every team with a crystal-clear playbook on what’s OK and what’s not.
Deploy Guardrails: Fini’s Live Enforcement Layer
Use Fini to:
Block access to unauthorized tools
Auto-flag sensitive terms (e.g., credit card, passport)
Monitor queries for signs of misuse
Real-time dashboards track violations and trends.
Goal: Move from reactive to proactive risk management, in real time.
Continuous Monitoring: Always-On Visibility
Set up 24/7 usage dashboards and alerts for policy violations.
Share weekly usage trends with compliance and ops.
Run quarterly AI usage audits to catch gaps.
Goal: Confirm policies are followed and not filed away and forgotten.
Ongoing Optimization: Stay Ahead of the Curve
Monitor new AI tools gaining popularity with agents.
Update sandbox tests, policy lists, and approved toolkits quarterly.
Use usage data to improve training and onboarding.
Goal: Treat governance as a living system, not a one-time fix.
Want to see this in action? 👀 Book a Guardrails Suite walkthrough
Looking for more accuracy tips? Read how how Fini achieves 95%+ AI accuracy.
Case Studies: Lessons from the Field
✅ Global Fintech Success
Results: 94% drop in Shadow AI events, $1.2M saved, +12-point CSAT improvement
❌ Mid-Sized E-Commerce Crisis
Issue: Agent used ChatGPT to handle 45,000 customer queries
Outcome: $4.67M in regulatory fines and churn impact
Both examples are anonymized composites drawn from Fini's governance engagements, reflecting patterns seen across the 200+ rollouts referenced above.
ROI: Governance That Pays for Itself
Benefit | Annual Value Gained |
|---|---|
Data Breach Prevention | $331K |
Regulatory Fine Avoidance | $90K |
Transaction Fraud Reduced | $91K |
Brand Trust Preservation | $93K |
Legal Investigation Savings | $22K |
Total Annual ROI | $629K+ |
Implementation with Fini costs less than $55K/year delivering >10X return. These ROI figures come from Fini's internal analysis of governance rollouts across 200+ organizations, benchmarked against the cost categories above.
See the framework in action
Get a free Shadow AI audit
Go live with Fini Guardrails in 14 days
Relevant Resources & Credible References
Don’t wait for a costly breach to take action. Secure your support operation today with Fini.
Ready to strengthen your support operations with strong Shadow AI governance?
FAQs
What tools constitute Shadow AI?
Shadow AI tools are any generative AI services (like ChatGPT, Claude, Gemini) used by employees without explicit company authorization, typically to expedite tasks or bypass official processes.
How frequently should governance reviews occur?
Governance reviews should ideally occur quarterly to promptly handle new risks or immediately after major AI-related changes within the organization.
Is Shadow AI usage illegal?
Shadow AI itself isn’t inherently illegal, but unauthorized use of AI can lead to regulatory violations, data breaches, and compliance issues that could have legal repercussions.
Can small businesses implement this framework easily?
Absolutely. The framework is scalable and adaptable to suit businesses of any size, with straightforward steps that can be adjusted according to organizational resources.
What is the first step to identify Shadow AI in my organization?
Start with a thorough audit involving employee surveys, network traffic analysis, and software usage monitoring to accurately gauge the presence and scope of Shadow AI.
Can we automate Shadow AI detection?
Yes, automation is possible through monitoring software, AI-driven analysis tools, and network scanning solutions, which help in real-time detection and alerting.
Are there specific industries most at risk from Shadow AI?
Industries handling sensitive data, such as finance, healthcare, e-commerce, and telecommunications, are especially vulnerable due to strict compliance requirements and the sensitive nature of customer information.
How do I communicate the importance of AI governance to employees?
Regular training sessions that stress real-world scenarios, clear communication of risks, benefits, and implications for security and compliance effectively convey the importance of governance.
Does Shadow AI affect customer trust?
Yes, unauthorized AI use can severely impact customer trust, especially if sensitive data is mishandled or leaked, resulting in long-term reputational damage.
Can governance frameworks completely eliminate Shadow AI risks?
Complete elimination isn’t feasible; however, strong governance frameworks greatly minimize risks through proactive management and continuous monitoring.
How do we automate post-purchase support without hurting CSAT?
The CSAT risk in post-purchase automation is almost always a governance gap, not the automation itself: agents deflect instead of resolve, or policies aren’t connected to the AI. Fini handles returns, refunds, and cancellations as agentic workflows connected to your billing system, OMS, and policy engine, so the agent takes the action instead of describing it. The same guardrails that stop Shadow AI misuse in this framework are what keep automated refunds within policy limits.
How do we assess the long-term stability of an AI support vendor before a deep integration?
Start with the basics: audited financials or a credible funding runway, named enterprise customers you can reference, and a clear data portability clause in the contract so you are not locked in if the vendor fails. Ask for SOC 2 Type II and any compliance certs relevant to your industry, since self-attested claims carry no weight during an audit. Check whether pricing is tied to resolved tickets instead of seats, which aligns vendor incentives with your outcomes. Finally, confirm the vendor can show a live production deployment at a company your size, and not merely a pilot. If they cannot answer those four questions clearly, the integration risk is too high.
Should our legal team be involved in AI governance?
Involving your legal team is important for making sure that all AI use complies with applicable laws and regulations, reducing legal risks and aiding in policy formulation.
What specific roles should oversee Shadow AI governance?
Key roles include IT security professionals, compliance officers, risk managers, and departmental managers who have clear oversight and accountability responsibilities.
How can support teams scale their customer base without growing headcount?
Deploying an autonomous AI support agent lets your existing team handle a rising ticket volume by resolving repetitive, high-frequency requests without adding agents. Fini resolves 90% of tickets autonomously at a per-resolution cost that drops as volume grows, so the marginal cost of serving each new customer falls instead of rising in step with headcount.
What common mistakes should we avoid when implementing AI governance?
Common mistakes include unclear policies, insufficient employee training, poor communication of governance expectations, and inadequate monitoring and enforcement mechanisms.
Can Shadow AI be beneficial in some cases?
Although initially appearing beneficial by boosting productivity, Shadow AI poses serious long-term risks including compliance violations and security vulnerabilities, outweighing short-term gains.
How do regulatory bodies view Shadow AI?
Regulatory bodies consider Shadow AI a serious compliance and security risk, advocating strong governance and clear oversight to manage potential negative consequences.
Are open-source AI tools riskier compared to commercial solutions?
Open-source AI tools can be riskier due to potentially less rigorous security controls, lack of structured vendor support, and limited compliance assurances compared to commercial solutions.
How can remote teams better manage AI governance?
Remote teams can effectively manage AI governance through strong digital monitoring solutions, regular virtual training sessions, clear remote work policies, and proactive communication channels.
How important is documentation in Shadow AI governance?
Documentation is critical, providing transparency, aiding compliance audits, and making certain that governance measures are well-understood, consistently implemented, and verifiable.
Can AI governance policies be integrated with existing IT policies?
Integrating AI governance with existing IT policies is strongly recommended, promoting consistency, ease of management, and full coverage across all technology use.
What should we do if we find active Shadow AI usage?
Immediately investigate the extent and impact, enforce corrective actions including temporary suspension of involved tools, conduct retraining, communicate transparently with staff, and update governance practices accordingly.
What compliance certifications support a Shadow AI governance rollout?
Fini is certified across the full stack required for heavily overseen industries: SOC 2 Type II, PCI DSS Level 1, ISO 27001, GDPR, HIPAA-compliant, BAA-eligible, and CCPA. These certifications mean your governance rollout is backed by independently audited controls, not self-attested claims. For fintech and healthcare operators, this directly covers the AI compliance exposure Shadow AI creates.
Will an AI customer support service actually sign a BAA?
Yes, when the vendor is HIPAA-compliant and BAA-eligible instead of just “HIPAA-ready.” Fini is HIPAA-compliant and BAA-eligible, and signs a Business Associate Agreement as part of onboarding for healthcare customers, so PHI moving through the agent is covered by a signed BAA, not a marketing claim.
Is compliance documentation or a trust center available for enterprise and FSI review?
Yes. Fini provides a full compliance documentation package for enterprise and financial services reviews, including audit reports, data processing agreements, and security questionnaire responses. Your legal, InfoSec, and procurement teams can request the package directly through the Fini team during the evaluation process.
Is there a real trial or money-back guarantee for AI support platforms?
Fini backs its Enterprise plan with a 90-day free pilot on live traffic, plus the Zero Pay Guarantee: 90% resolution in 90 days, or you pay $0. Send 1,000 real tickets and we’ll prove it on your data before you commit to a contract.
How does an AI-native support agent differ from a legacy ticketing system with AI bolted on?
Legacy ticketing systems like Intercom Fin add AI features on top of a workflow built for human routing, queuing, and manual review. The AI sits inside the ticket flow instead of owning it, so resolution rates stall because every response still depends on the same handoff logic underneath. Fini is built as an autonomous AI support agent from the ground up: the agent owns the conversation end to end, executes agentic workflows, and resolves tickets without a human in the loop for the cases it is trained on. When a team's resolution rate has plateaued at 30 to 50 percent on a bolted-on tool, the ceiling is usually architectural, not a training problem. Replacing the layer on top of a legacy system with Fini removes that ceiling and replaces it with a 90 percent resolution commitment backed by the Zero Pay Guarantee.
How is data residency handled?
Fini supports configurable data residency so customer data stays within your required geographic boundaries, with dedicated DPA and encryption controls available at the Enterprise tier. Residency options and regional configurations are confirmed during onboarding and documented in your data processing agreement. Contact the Fini team to confirm the right configuration for your compliance requirements.


Co-founder